Investigation · Validated
Integration Capability Assessment
Mapped authentication behavior, documentation gaps, and a responsible integration path.
One operator-focused system for recurring facilities-planning workflows.
Workbench grew from recurring planning work that moved between tools, files, and repeated handoffs. My focus was bringing those steps into a shared operating pattern, with a preview of the changes, validation before action, and a path to recover when something went wrong.
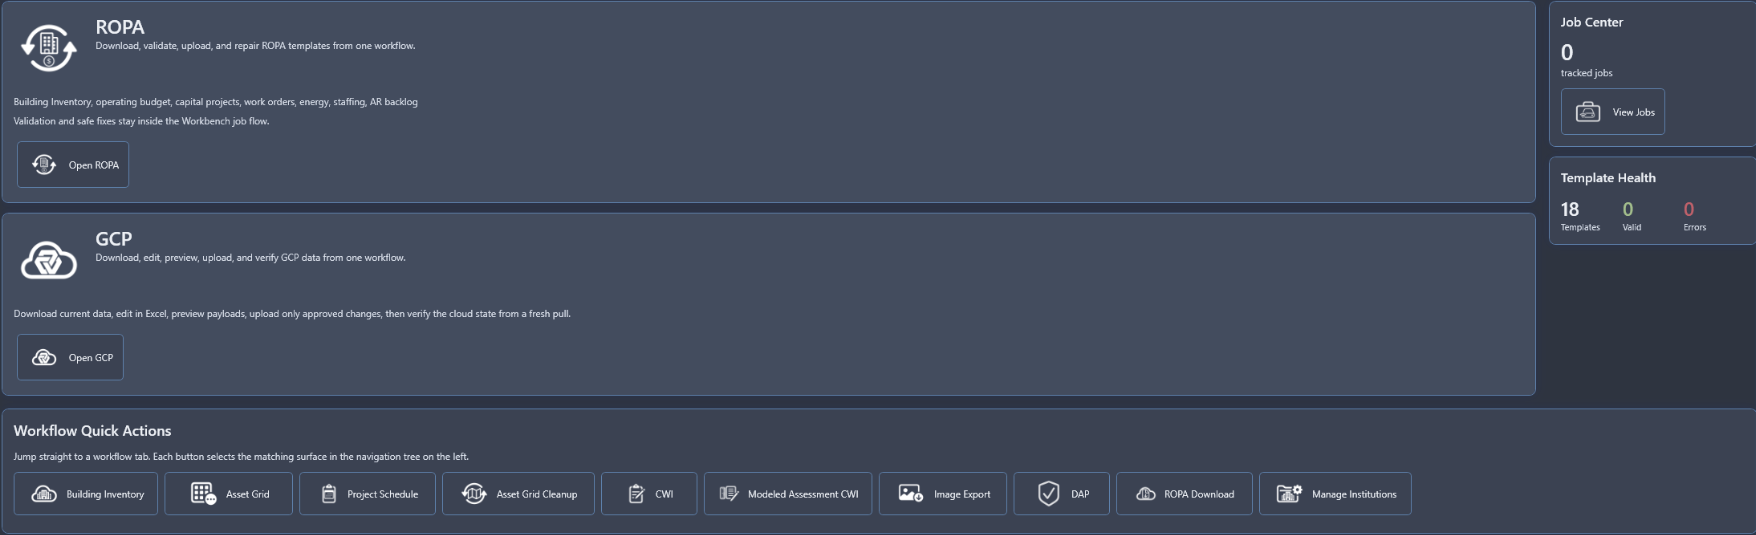
The work spans multiple capabilities and iterations. Evidence is described at the capability level; a label on one workflow does not establish the status of every version or historical use. Measured savings are not claimed here.
Guided actions through a desktop shell and spreadsheet extension.
Preview, rules, field guards, visible state, and recovery paths.
Modular transforms and connectors behind a stable operator pattern.
The systems of record remain authoritative at the integration boundary.
Existing systems remain authoritative
| Dimension | Definition | Evidence state |
|---|---|---|
| Efficiency | Median task time before and after | Measure during controlled runs |
| Throughput | Items completed per active minute | Instrument per capability |
| Quality | Validation issues intercepted | Record per run |
| Reliability | Completed runs divided by initiated runs | Instrument failure states |
| Adoption | Repeat users and completed runs | Track during pilot |
| Coverage | Share of target workflow supported | Map per capability |
| Maintainability | Validation, defects, and recovery evidence | Expand the test record |
Operational context
Planning work often moved between browser-based tools, spreadsheets, manual transformations, and repeated handoffs. Routine changes were slow to execute consistently, difficult to validate safely, and difficult to recover when something went wrong.
Isolated scripts could remove individual repetitions, but they could not create a coherent operating model. The Workbench is the product outcome: one shared surface, with modular lanes for each recurring workflow and a common language for preview, validation, execution, and recovery.
Select a capability to see the operational job it owns, the evidence that currently exists, and the measurement needed to prove its value.
ContributionWorkflow discovery Requirements Architecture Implementation Testing Cross-functional alignment
Product and architecture choices
Preview, controlled values, and period guardrails make unsafe state visible before a return operation.
Each integration respects the identity and authorization model of the enterprise system it connects to.
Failures need a legible next action. Recovery and repair are designed alongside the successful path.
The shell, validation patterns, and operator language stay consistent while each workflow lane evolves independently.
What is safe to claim today
The product has working workflows and validation evidence. Outcome metrics remain deliberately marked as measurement work until they have a baseline, sample, and period.
Next operating milestone
Capture duration, item count, completion, failure, and validation count without sensitive payloads.
Compare representative runs against a documented manual baseline.
Use recovery, reliability, and repeat-use evidence to prioritize the next change.
Broaden workflow coverage without weakening the shared operating model.
Mapped authentication behavior, documentation gaps, and a responsible integration path.
Turned a repeatable creation task into a structured, working workflow.
Converted recurring QC findings into ownership, validation, and correction rules.
This case study is intentionally public-safe. It describes the product, operating model, and my contribution without reproducing employer or client systems, data, credentials, or internal endpoints.